Challenge
The firm needed to extend its existing Okta environment to external co-counsel accessing Relativity without introducing new risk. It came to the engagement with a list of open issues, outstanding technical questions, and concerns about potential security gaps.
Key needs included defining the SPA architecture and realm assignment logic, separating internal and external login paths, and establishing customer attributes in Okta Universal Directory. The firm also needed guidance on MFA reset and support workflows and on managing the lifecycle of external access, with the goal of running the environment independently.
Solution
Conducted Discovery Sessions
Led deep-dive sessions with stakeholders to review the firm’s current state, resolve outstanding technical questions, and finalize the implementation plan.
Designed and Built the Secure Partner Access Configuration and Architecture
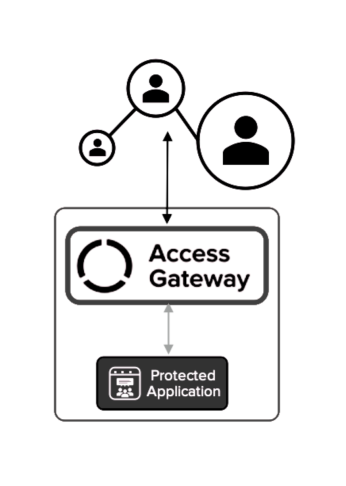
Finalized the target SPA model and configured dedicated partner realms to support co-counsel access to Relativity. This established completely separate login paths for internal and external users, driving assignment logic and external identities through precise mappings between Okta attributes and the firm’s Universal Directory (UD).
Designed MFA Reset and Support Workflows
Provided critical advisory guidance on MFA reset and support workflows, strengthening security at the exact point where users most frequently encounter friction and need assistance.
Designed MFA Reset and Support Workflows
Provided critical advisory guidance on MFA reset and support workflows, strengthening security at the exact point where users most frequently encounter friction and need assistance.
Defined an Access Expiration Strategy
Defined lifecycle processes built on attribute updates and group-based entitlements. Because the firm did not hold Okta Workflows licenses, BeyondID guided the team through alternative approaches they could easily manage on their own.
Guided Lifecycle Management Processes
Defined lifecycle processes built on attribute updates and group-based entitlements. Because the firm did not hold Okta Workflows licenses, BeyondID guided the team through alternative approaches they could easily manage on their own.
Delivered Best Practices and Knowledge Transfer
Reviewed industry best practices, answered the firm’s specific operational questions, and transferred deep technical knowledge throughout the engagement so the team could operate independently.
Impact
Secure, Structured External Collaboration
The firm’s initial security concerns were fully resolved through defined access policies, robust group assignment models, and secure workflows for MFA resets, resulting in a more secure Okta environment.
Stronger Security Posture
The firm’s initial security concerns were fully resolved through defined access policies, robust group assignment models, and secure workflows for MFA resets, resulting in a more secure Okta environment.
Faster Time to Value
An engagement originally expected to take several months was successfully completed in a matter of weeks, accelerating the firm’s return on investment.
A More Self-Sufficient Identity Team
Every outstanding technical question on the firm’s list was answered, and the “teach to fish” approach left the internal team fully confident in managing workflows and day-to-day identity operations.
A Clear Path for Governing Short-Term External Access
With an access expiration strategy covering time-bound limits, inactivity cleanups, and matter-based reviews, the firm is perfectly positioned to ensure external access exists only as long as it is needed.
An Improved Okta Tenant
Continuous best-practice guidance significantly strengthened the firm’s broader Okta tenant, boosting the overall efficiency and security of their day-to-day identity functions.